Foundational empathy
The project began by exploring how people perceive cybersecurity training and why it often fails to change behaviour. Initial research involved desk research, a short survey and an interview with a CREST-accredited cybersecurity professional.
Key points:
- Explored how people perceive cybersecurity training in practice.
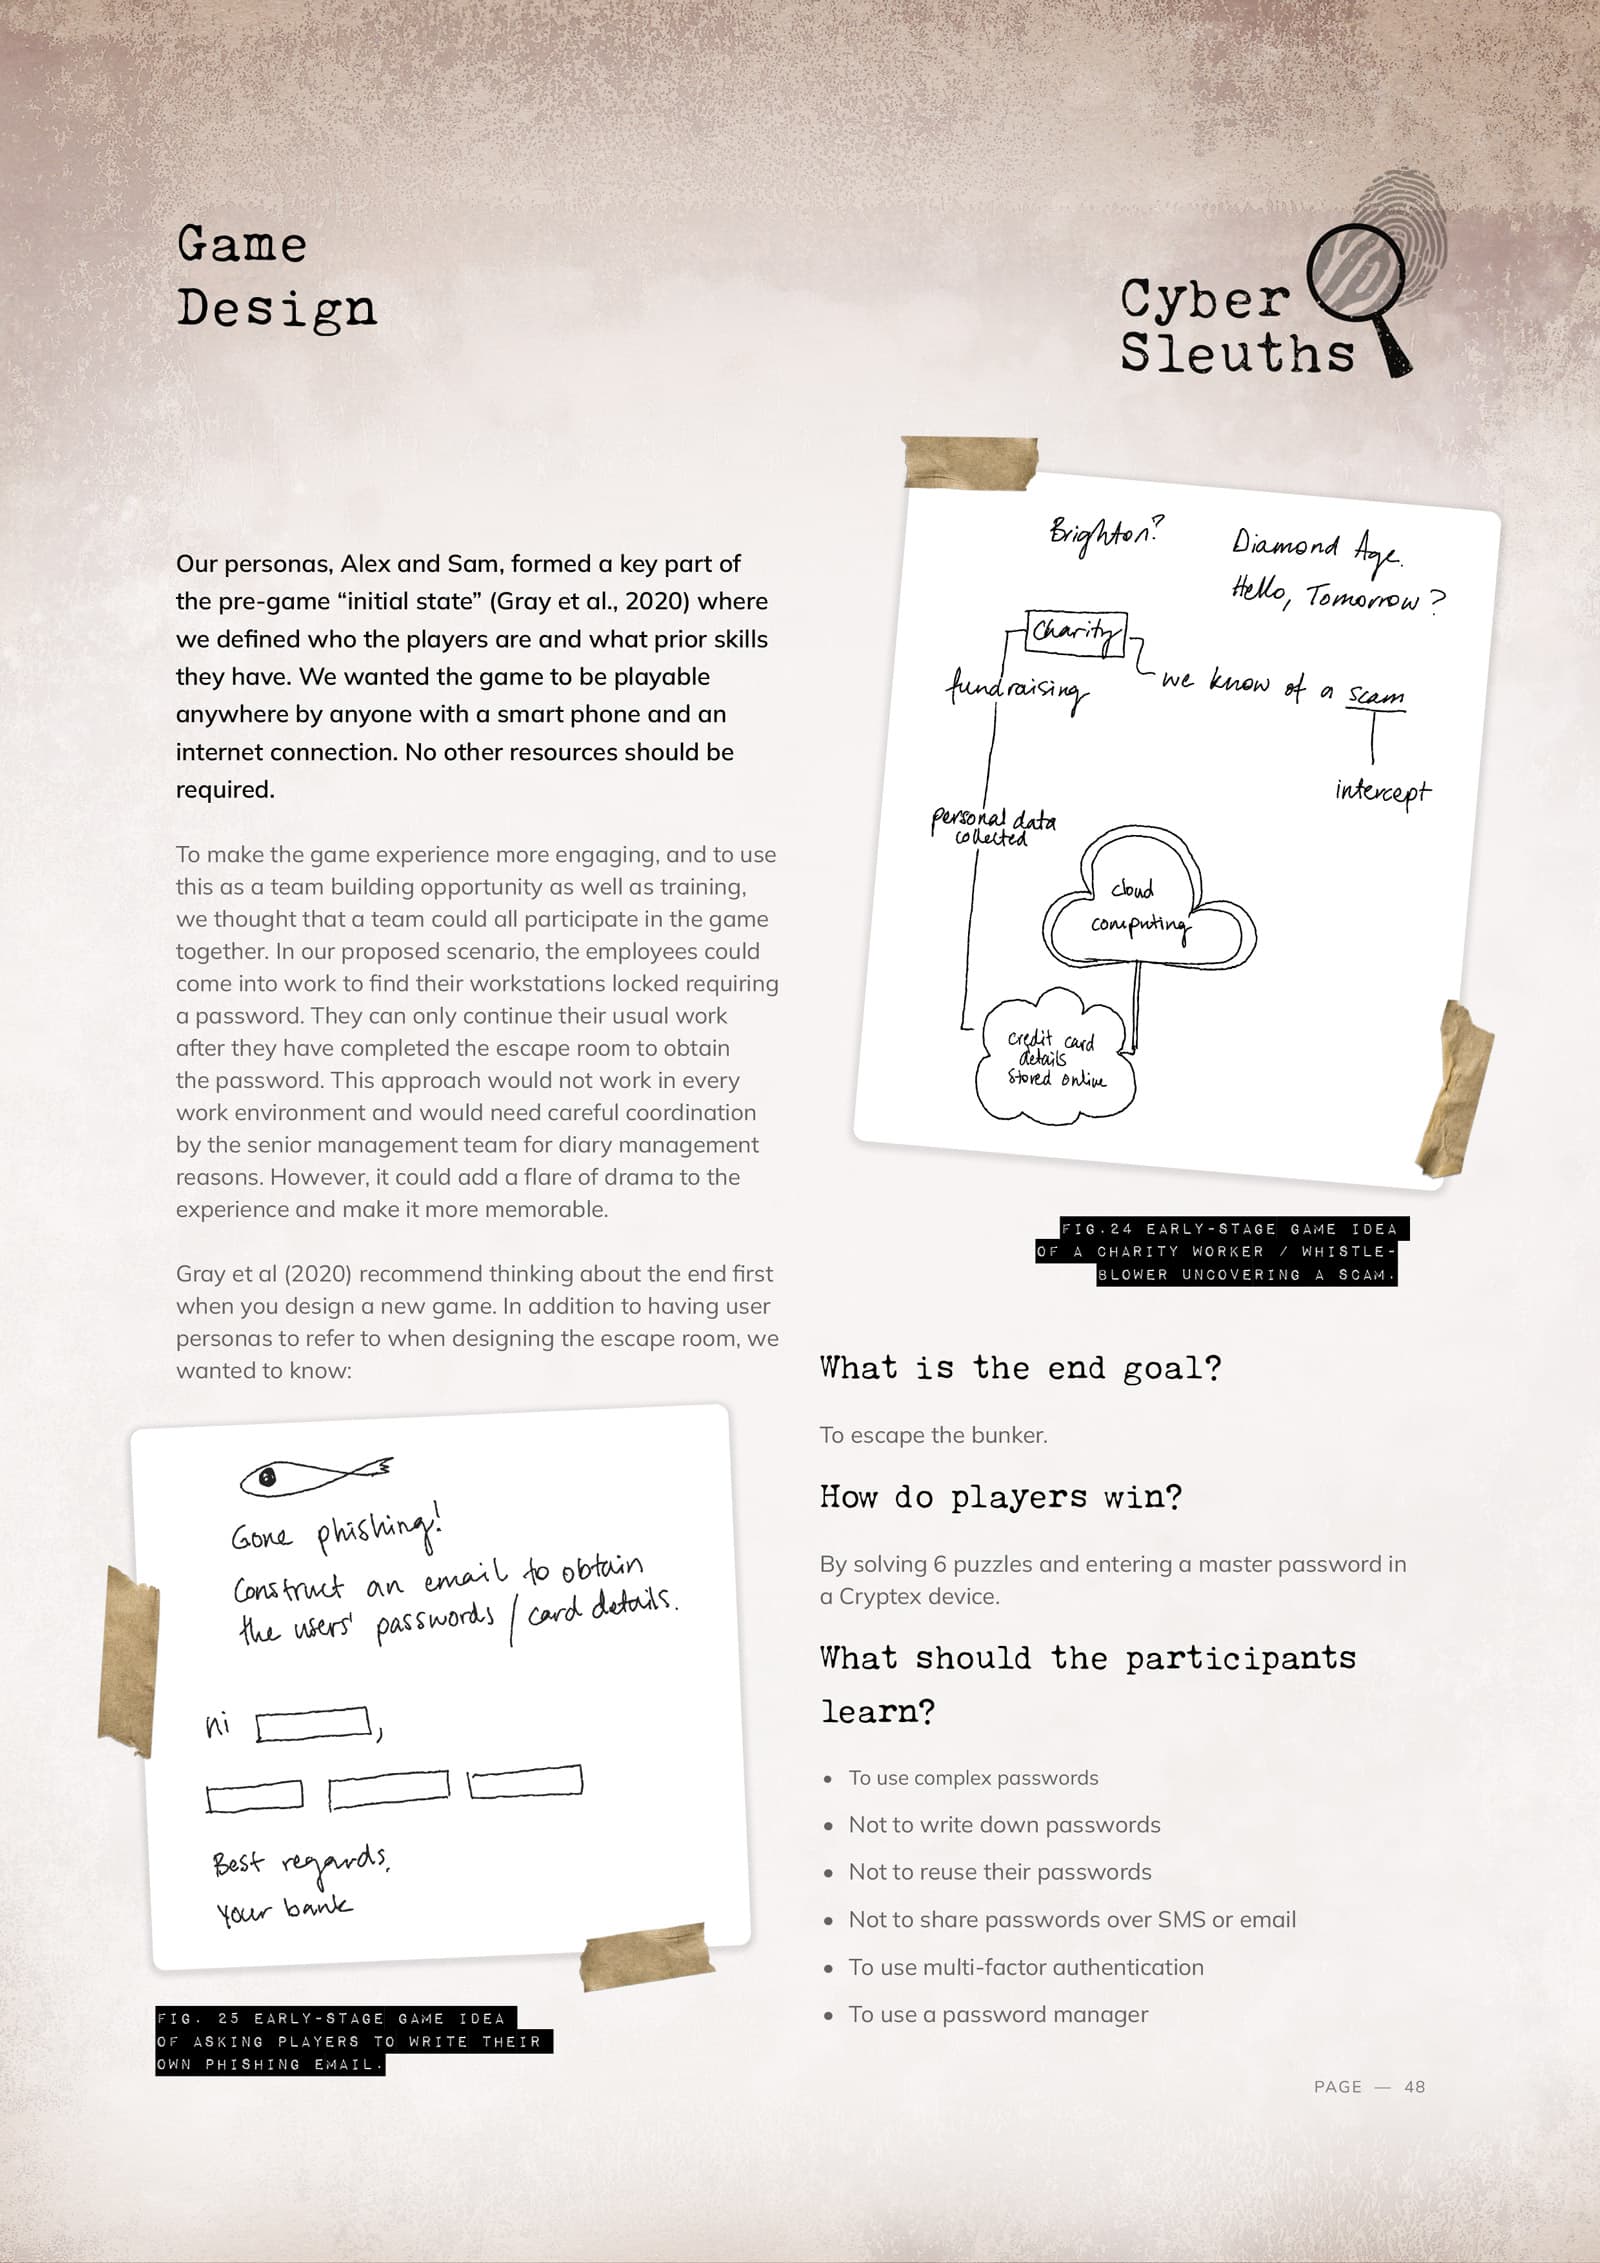
- Looked at why existing approaches struggle to change behaviour.
- Compared user attitudes with real-world security habits.
- Examined how training tools balance engagement and learning.
- Identified behavioural patterns that undermine traditional instruction.
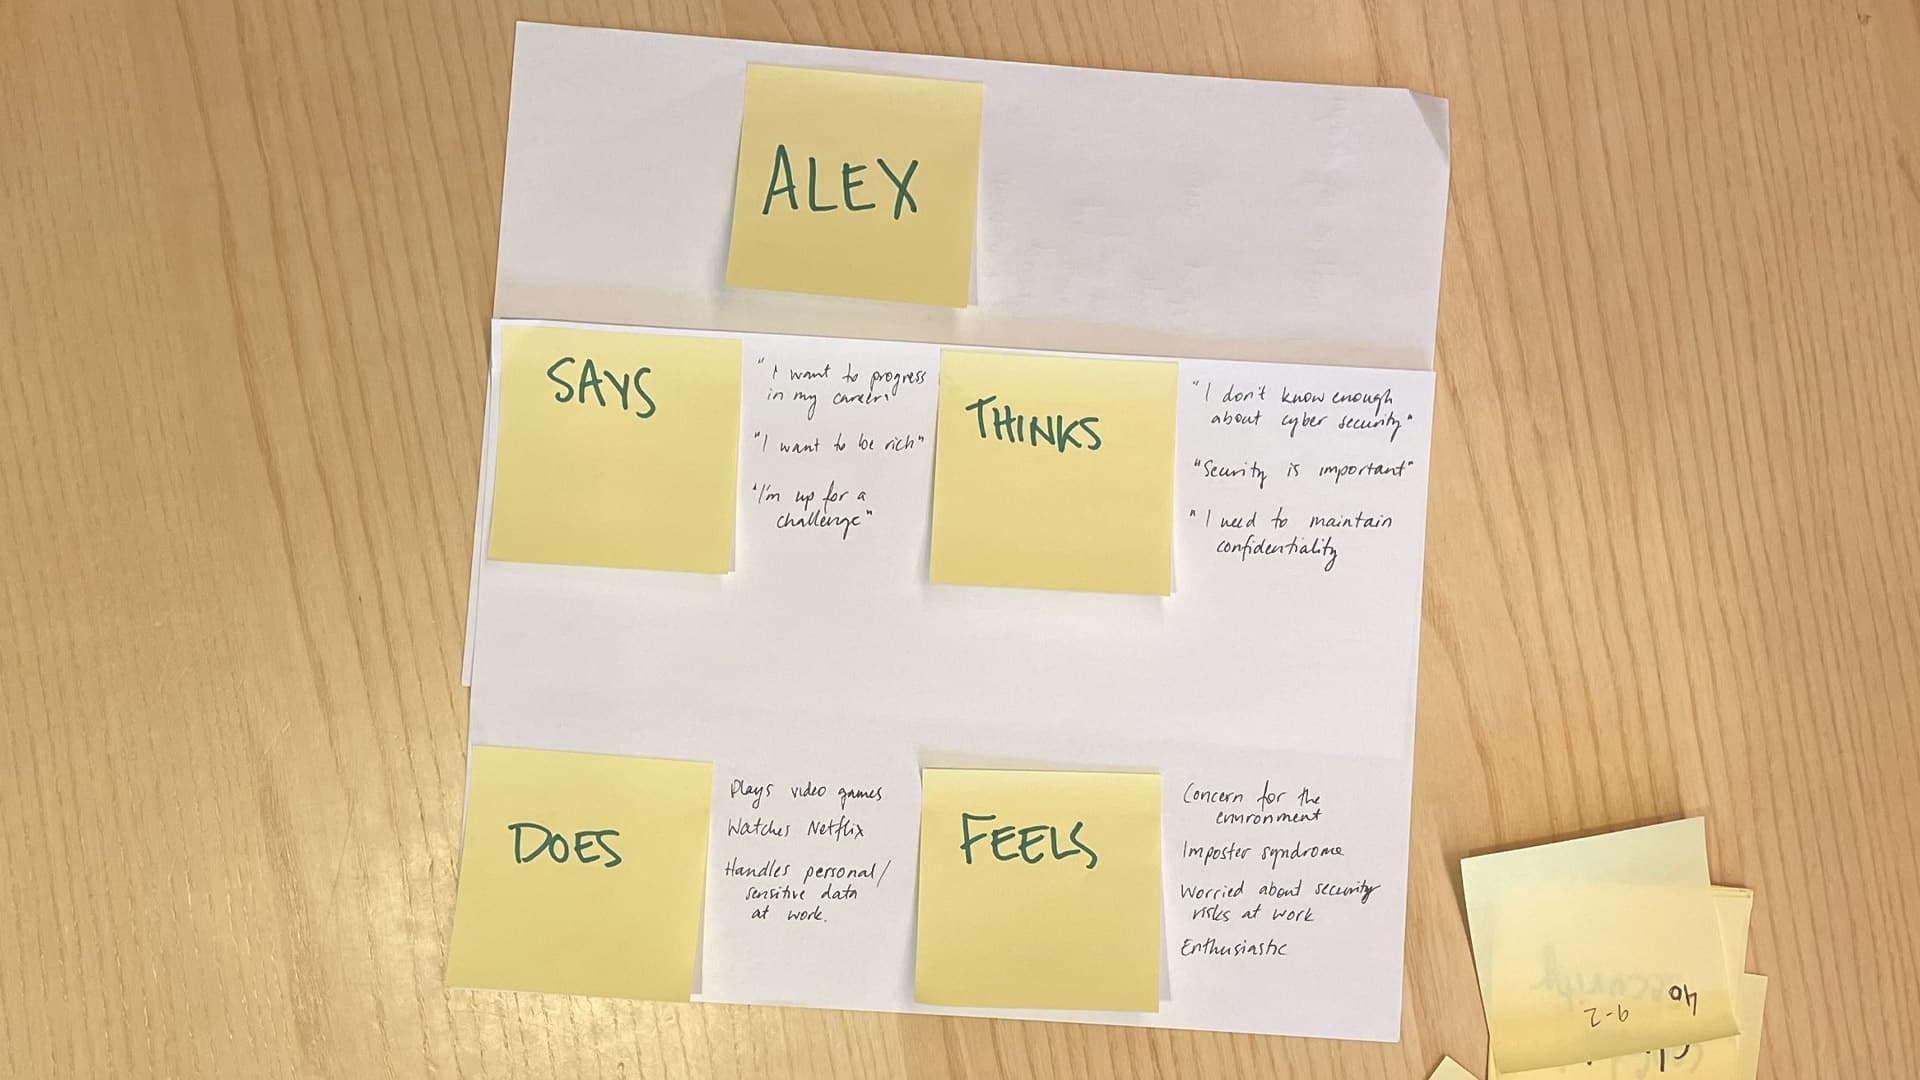
The survey revealed a recurring pattern. Participants generally rated their understanding of password security as high, but admitted to poor practices such as password reuse, predictable structures, and insecure storage. This suggested that a lack of information wasn’t the main issue. Instead, users believed they understood the risks and therefore disengaged from conventional training.


Limitations of existing training approaches
A review of existing cybersecurity training tools and escape-room-style learning experiences revealed a tendency towards either oversimplification or excessive complexity. Many focused on entertainment without verifying learning, while others prioritised instruction at the expense of engagement.
Behavioural reality and design constraints
The expert interview reinforced the tension. Real-world breaches, especially in small organisations, were rarely caused by advanced attacks. They were usually due to basic behaviours such as weak passwords, reusing passwords across services, and misunderstanding authentication processes.
This phase established a key constraint for the project. Any solution relying on lectures, instructions or self-directed learning would likely reproduce the same disengagement patterns seen in traditional training.